
Customer Risk Assessment Software in Singapore
Ready to Defeat Your AML Compliance Obstacles?
Citadel Brings Revolution with Secure Solutions to AML Compliance Problems
Customer risk assessment software in Singapore- Key Takeaways
- Customer risk assessment software in Singapore is a compliance technology that helps businesses evaluate client financial crime risks and comply with rules from the Monetary Authority of Singapore (MAS).
- Key features of customer risk assessment software include a configurable risk model, PF risk assessment capability, documented rationale per rating, automated periodic review and Integration with onboarding and screening
- Citadel365 supports Singapore compliance through customer risk assessment, PF risk evaluation, EDD workflows, and automated review tracking.
What Is Customer Risk Assessment Software?
Customer risk assessment software in Singapore is a compliance technology helping regulated entities apply a risk-based approach to customer due diligence. It can assign and document customer risk ratings based on relevant money laundering (ML), terrorist financing (TF), and proliferation financing (PF) risk factors, support enhanced due diligence for higher-risk customers, and schedule periodic reviews so that customer risk assessment remains updated throughout the business relationship.
MAS AML/CFT Notice requires MAS-regulated financial institutions to adopt a risk-based approach, taking into account their ML/TF and, where applicable, PF risks and applying controls that are proportionate to those risks.
An enterprise-wide risk assessment (EWRA) helps an entity identify and understand its overall ML/TF/ PF risks and determine appropriate controls. Customer risk assessments should then consider the relevant customer-specific risk factors and be supported by proper documentation rather than relying solely on an automated numerical score.
Why Customer Risk Assessment Software Matters in Singapore
Customer risk assessment software matters in Singapore because it helps regulated entities apply a risk-based AML/CFT framework more consistently, with documented assessments, risk-based reviews and clear audit trails.
Customer risk should consider relevant risk factors, be supported by documented reasoning, and be reviewed when appropriate rather than relying only on a numerical risk score.
The July 2025 amendments to the MAS AML/CFT framework clarified that money laundering risks include proliferation financing risks, bringing PF considerations into the risk assessment requirements applicable to MAS-regulated financial institutions.
How Does Customer Risk Assessment Software Work in Singapore?
Customer risk assessment software in Singapore automates the process of evaluating, scoring, and monitoring client financial crime risks to comply with MAS regulations.
Step 1: EWRA as the foundation
The enterprise-wide risk assessment helps the entity identify and understand its overall ML/TF/ PF risks across the relevant areas, including customer types, products and services, delivery channels, and geographic exposure. Customer risk assessment processes can then be aligned with the entity’s broader risk assessment and control framework. CRA software can help with proper documentation and version-tracked EWRA to support regulatory review.
Step 2: Customer risk scoring at onboarding
During onboarding, the platform helps assess the customer-specific configurable risk factors, including nationality, residency, customer type, product, delivery channel, PEP status, screening results and other relevant risk indicators. PF risk factors can also be incorporated into the assessment, aligning with the entity’s risk profile and applicable MAS requirements where relevant.
Step 3: Documented rationale
The software records the factors considered in determining the customer’s risk rating and can maintain the supporting rationale and assessment history. This creates an audit trail showcasing and supporting the decision made, compliance reviews, internal governance, and MAS supervisory examinations.
Step 4: EDD trigger and workflow
Where the customer risk is identified as high-risk, the platform automatically triggers enhanced due diligence workflows. Depending on the applicable requirements and risk assessment, this may include additional measures for PEPs, high-net-worth individuals and customers from high-risk jurisdictions. This may include collecting and reviewing the source of wealth or source of funds information, obtaining additional customer information, applying enhanced monitoring and obtaining the required senior management approval.
Step 5: Rating updates and audit trail
When the customer’s information changes, including new screening results, change in ownership or control, changes in products or services used, or other material changes in customer circumstances, the software can flag the customer for reassessment. These changes are recorded in the audit trails, and the history can be retained to support future MAS inspections.
Key Features of Customer Risk Assessment Software for Singapore
Customer risk assessment software in Singapore supports MAS-aligned frameworks, assesses risk with greater clarity, and automates key workflows while keeping the decisions traceable. Some of the key features include:
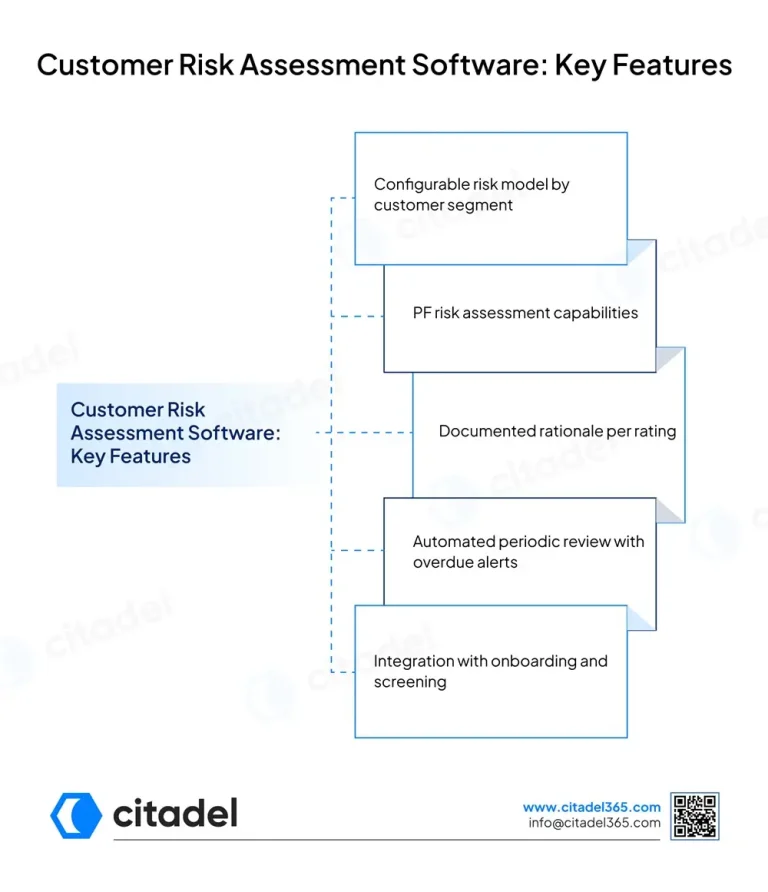
Configurable risk model by customer segment
CRA software enables configurable risk factors and weightings according to customer type, product, and segments. This allows banks, payment institutions, DPT service providers and other regulated entities to apply a risk-based customer assessment approach aligned with their applicable MAS requirements.
PF risk assessment capabilities
The software can incorporate relevant proliferation financing (PF) risk factors into the entity’s risk assessment framework. Relevant factors may include geographic exposure, customer activities, transaction patterns, and exposure to goods or sectors presenting PF risks.
Documented rationale per rating
The software helps in recording the factors considered in determining each customer’s risk rating and can retain supporting evidence and rationale; it helps in creating the audit trail and demonstrates the decision made to support regulatory examination and compliance review.
Automated periodic review with overdue alerts
The platform can schedule customer reviews according to the entity’s risk-based framework and applicable regulatory requirements. Higher-risk customers can be assigned more frequent reviews, while alerts can be generated for upcoming or overdue reviews before they become inspection findings.
Integration with onboarding and screening
Customer risk assessments can be connected with onboarding, KYC and screening processes; new customer information, screening results and other relevant changes can be used to flag customers for reassessment, helping connect the risk assessment with the wider AML/CFT compliance workflow.
How Citadel365 Customer Risk Assessment Software Supports Singapore Compliance
Citadel365 supports Singapore compliance through its customer risk assessment software that enables regulated entities to implement the MAS risk-based approach with document rationale, automated periodic reviews, and the proliferation financing risk dimension.
Citadel365 also includes an EWRA module that supports the assessment and proper documentation of ML/TF and PF risks. It helps entities maintain dated, version-tracked records for MAS examination and support internal governance.
Customer risk assessment software considers relevant risks, identifies PEPs, and can trigger EDD, while automatically scheduling customer reviews based on their risk level.
Each risk assessment, supporting rationale, review activity, and EDD workflow is well recorded with an audit trail to support compliance reviews or regulatory examinations, providing compliance teams with a structured record of how the customer risk was assessed, reviewed, and updated over time.
Simplify Customer Risk Assessment in Singapore
Citadel365 helps in assessing ML, TF, and PF risks, supports EDD, and keeps every risk decision traceable.
FAQs About Customer Risk Assessment Software in Singapore
Customer risk assessment software is a digital compliance tool that helps Singapore regulated entities evaluate and score the ML/TF and other financial crime risk posed by customers, while supporting risk-based due diligence, monitoring, and periodic reviews.
Proliferation financing (PF) means providing funds or financial services that support the spread of weapons of mass destruction. From 1st July 2025, revised MAS AML/CFT Notices clarified that money laundering risks include proliferation financing risks, bringing PF considerations within the applicable ML/TF risk assessment framework.
An EWRA helps an entity identify and understand its overall financial crime risks. Under the MAS framework, relevant entities must consider ML, TF, and PF risks, along with factors such as customers, products and services, channels and geography.
Customer risk assessment software supports Monetary Authority of Singapore supervisory inspections by providing an objective, verifiable, and audit-ready framework that demonstrates how the institution applies its risk-based approach.
Arjun is the Co-founder and CEO of Citadel, where he leads the company’s vision across technology, business, and regulations. He brings over a decade of experience in building and scaling technology ventures. Arjun holds a B.Tech. in Information Technology and a Master’s in Management, supported by his certification as a Financial Crime Specialist, an uncommon combination that allows him to balance innovation with regulatory requirements.
Having advised leading banks and financial institutions on digital solutions and compliance technology, Citadel continues to grow with an ambition.